Imagine stepping into a coffee shop, buying a latte with a crypto‑card, and feeling the rush of anonymity wash over you, only to realize the transaction left a breadcrumb trail you didn’t even see. Crypto‑cards promise the convenience of a plastic swipe and the secrecy of blockchain, but hidden data flows can expose patterns that savvy analysts decode in a heartbeat. Dive into the mechanics early, and you’ll spot the gaps before they become headlines. For a deeper dive, check out cryptocardstips.com and start fortifying your approach.
Every time you tap, a network handshake occurs, pinging servers that log timestamps, IP addresses, and device fingerprints. Those logs sit quietly until a subpoena or a data breach pulls them into the public eye. The illusion of privacy is fragile; it shatters when merchants collude or when payment processors aggregate data across thousands of users. Recognize that each swipe is a conversation, not a whisper, and your strategy must treat it as such.
Understanding the Data Trail of Crypto Cards
While most users believe a crypto‑card erases identity, the reality is that on‑chain addresses can be linked to off‑chain profiles through KYC data supplied to issuers. Even if the blockchain itself masks your name, the issuer’s database often retains personal documentation, turning anonymity into a conditional promise. A few careless steps—like reusing the same address for multiple purchases—connect the dots more quickly than a detective with a magnifying glass.
The moment a transaction confirms, multiple nodes broadcast the event to peers, each logging the data in their own ledger. Those nodes, spread across jurisdictions, may comply with different privacy statutes, creating a patchwork of exposure risks. Some jurisdictions enforce mandatory data retention, meaning your purchase history could linger for years, waiting for an opportunity to be misused. Pay attention to the geography of the nodes you interact with; it matters more than you think.
Because crypto‑card providers often bundle analytics services, they harvest granular data to refine marketing tactics. This secondary layer of insight can be sold or subpoenaed, turning a simple purchase into a data point in a larger profile. Think of it as a two‑tiered privacy model: the blockchain layer and the corporate layer. Neglecting either invites compromise, especially when the corporate layer is less regulated.
Nonetheless, the choice of card can dramatically shift your exposure. Some issuers embed mixers or adopt privacy‑first architectures, masking transaction origins before they ever hit the public ledger. Others operate as thin wrappers around traditional payment rails, inheriting every weakness of those systems. Scrutinize the provider’s whitepaper, and look for explicit mentions of privacy‑enhancing technologies, not just vague buzzwords.
Choosing the Right Wallet Architecture
In the landscape of crypto‑cards, the wallet’s underlying structure dictates how much control you retain over your data. Custodial wallets place the private key in the hands of the service, meaning you trust their security practices entirely. Non‑custodial wallets hand you the key, but also the responsibility for safe storage and transaction signing, which can be both empowering and terrifying.
Thus, a hybrid approach often emerges as the sweet spot: the card itself operates on a hierarchical deterministic (HD) wallet, generating fresh addresses for each purchase, while the master seed remains encrypted on a secure element. This design slices the attack surface, preventing a single breach from exposing the entire transaction history. Look for cards that advertise seed encryption and hardware isolation as non‑negotiables.
Hardware Isolation vs. Software Encryption
However, many manufacturers market “software encryption” as if it mirrors hardware isolation, but the two are worlds apart. Software encryption can be reverse‑engineered, especially if the firmware is publicly available or if the device runs a generic operating system. Hardware isolation, by contrast, locks the cryptographic operations inside a tamper‑resistant chip, making extraction significantly harder. Choose cards that detail the chip model and the security certifications they hold.
As the market matures, some providers adopt multi‑signature schemes, requiring two independent keys to approve a spend. This adds a layer of resilience: even if one key is compromised, an attacker still needs the second to move funds. Multi‑sig setups also enable you to split the signing authority between a personal device and a backup, ensuring continuity without sacrificing privacy. Embrace multi‑sig if you can tolerate the slightly higher transaction fees.
Network Interactions and Anonymity Sets
Suddenly, the network you connect through becomes a silent witness, recording latency, routing paths, and sometimes even your geographic location. Using a public Wi‑Fi hotspot for a crypto‑card transaction can expose your IP address to the merchant, who may log it alongside the purchase. VPNs and Tor can obscure the origin, but they also add latency and occasionally trigger fraud alarms.
Typically, the size of the anonymity set—the pool of users indistinguishable from you—depends on how many others employ the same mixing or privacy protocol. Small pools are easy to de‑anonimise; large pools provide a buffer of plausible deniability. When selecting a card, examine whether it routes transactions through a mixer, and if so, how many participants regularly use that mixer. Bigger is better, but only if the mixer is reputable.
Practically, you can increase your anonymity set by rotating between multiple cards, each linked to distinct on‑chain addresses. This practice breaks the linear chain of purchases, forcing analysts to treat each card as a separate entity. The downside is managing multiple seeds and ensuring you don’t lose access to any of them. Use a secure password manager to track seed locations without storing them in plaintext.
Rarely does a single transaction reveal the whole story, but cumulative patterns do. If you habitually buy coffee every morning at the same cafe, the merchant can aggregate that data over weeks and infer habits, even without knowing your name. Vary your purchase times, merchants, and even the amounts you spend to blur the patterns. The more randomness you inject, the fuzzier the final picture becomes.
Operational Security Practices
Consequently, everyday habits matter as much as technical choices. Never reuse the same address for multiple distinct purchases unless you’re comfortable with the resulting linkability. Always verify the card’s firmware version before each use, ensuring you’re not running a compromised build that leaks keystrokes or private keys to an unseen server.
Ultimately, device hygiene extends beyond the card itself. Secure the companion app with a strong, unique password, enable biometric locks, and disable any background data syncing that isn’t essential. A compromised phone can become the conduit through which attackers siphon your keys or monitor transaction confirmations, bypassing the card’s built‑in protections entirely.
Frequently, users underestimate the power of social engineering. Phishing attempts that mimic official support channels can coax you into revealing seed phrases or OTP codes. Treat any unsolicited request for such information as hostile. When in doubt, contact the provider through verified channels listed on their official website, not through the link in an email.
Surprisingly, the simplest protective measure—keeping a physical backup of your seed phrase in a secure location—often prevents the most catastrophic losses. Fireproof safes, sealed metal plates, or even a sealed envelope stored in a bank deposit box can safeguard against device failure or loss. The backup should be stored offline, far from any networked device, to maintain true isolation.
Future‑Proofing Your Privacy Strategy
Generally, the crypto‑card ecosystem evolves faster than regulations, meaning today’s privacy‑friendly features may become tomorrow’s liabilities. Keep an eye on legislative trends around digital payments, especially those pushing for mandatory transaction reporting. Anticipate changes by selecting cards that can adapt—those that support firmware updates without sacrificing cryptographic isolation.
Personally, I recommend allocating a portion of your crypto portfolio to privacy‑focused assets that naturally blend with other transactions, like privacy‑enhanced stablecoins. By moving value through assets that already enjoy a high degree of anonymity, you add an extra layer of obfuscation to your card usage. This isn’t a silver bullet, but it nudges the signal-to-noise ratio in your favor.
Straightforwardly, adopt a habit of regular audits: review your transaction history, check for any unexpected address reuse, and confirm that the card’s security settings remain optimal. Treat each audit as a health check for your anonymity, catching leaks before they become breaches. The discipline of periodic review is the quiet guardian of long‑term privacy.
Actually, the final piece of actionable advice: before you make your next swipe, power up a trusted VPN, verify your card’s firmware, and generate a fresh address—then spend. That three‑step routine folds all the principles discussed into a single, repeatable habit that shields you from the majority of privacy pitfalls.
独自に開発した
タイピングソフトを販売しております。
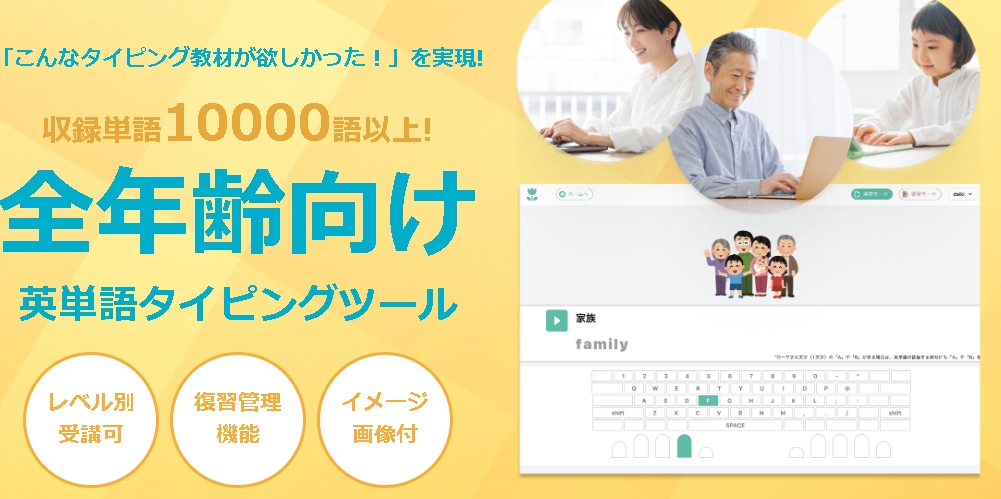
単語学習、聞き取り学習、タイピング練習はもちろん。
できなかった部分だけを重点的に学習できるように復習機能もついています。
また、中1レベルからTOEIC900点クラスまで網羅している為
無料お試し版がご利用いただけますので